Capstone Technologies Group LLC Capstone Technologies Group LLC
  • Home
  • Services
    • Managed IT Solutions
    • Cybersecurity Services
    • Data Protection & Recovery
    • VoIP Solutions
    • Website Solutions
  • Industry Solutions
    • Legal IT Solutions
    • Medical IT Solutions
    • Financial IT Solutions
    • SMB IT Solutions
    • Non Profit IT Solutions
  • Resources
    • Blog
    • White Papers
    • Threat Intelligence Center
  • About Us
    • Who We Are
    • Client Testimonials
    • Case Studies
  • Threat Intelligence Center
  • Pricing

Springfield, OH · Call (937) 319-1211

Facebook
LinkedIn
Mastodon
Bluesky
Capstone Technologies Group LLC Capstone Technologies Group LLC
  • Home
  • Services
    • Managed IT Solutions
    • Cybersecurity Services
    • Data Protection & Recovery
    • VoIP Solutions
    • Website Solutions
  • Industry Solutions
    • Legal IT Solutions
    • Medical IT Solutions
    • Financial IT Solutions
    • SMB IT Solutions
    • Non Profit IT Solutions
  • Resources
    • Blog
    • White Papers
    • Threat Intelligence Center
  • About Us
    • Who We Are
    • Client Testimonials
    • Case Studies
  • Threat Intelligence Center
  • Pricing

Contact Us

Threat Intelligence Center

Blueprint schematic of build pipeline credential theft and data exfiltration from a poisoned software dependency

Australia Arrests Alleged TeamPCP Hackers Behind Supply-Chain Attacks

Australian authorities have arrested individuals alleged to be members of TeamPCP, a group tied to supply-chain attacks. Arrests do not remove the underlying exposure: supply-chain compromise turns trusted vendor software and update channels into a delivery path. For firms holding regulated client data, it is worth reviewing which third parties hold access.
Schematic of dark web SSN lookup: free identity search unlocking a paywalled executive record for impersonation

Identity-as-a-Service Markets Sell Executive SSNs Through Bankomat and Xilo

Identity-as-a-Service describes the commodification of stolen personal data on dark web marketplaces, where Social Security numbers and supporting identity records tied to executives are packaged for repeat buyers rather than sold in one-off dumps. Marketplaces and tools identified in this analysis include Bankom, Bankomat, PeopleFinder and Xilo.
Diagram of string-array encoding, control-flow flattening and eval execution sink used by phishing kit obfuscation

JavaScript Obfuscation Evolves From Party Trick Into Phishing Kit Tooling

JavaScript obfuscation began as something close to a party trick, a way to make readable code unreadable without changing what it does. That same technique now appears as standard tooling in phishing kits, where hidden script logic makes malicious pages harder to inspect and classify.
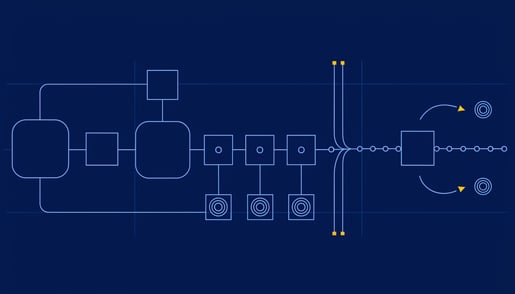
Circuit schematic of Spark RAT chain: DLL sideloading, PNG shellcode, AMSI and ETW telemetry cut, kernel driver abuse

Spark RAT Campaign Abuses OPSWAT ardrv.sys Driver to Kill Security Tools

A Spark RAT campaign aimed at Cambodia delivers the implant through Inno Setup installers and pairs it with a vulnerable signed driver. Operators load ardrv.sys, the OPSWAT AppRemover driver based on the Zemana Anti-Malware SDK and tracked as CVE-2026-36425, to terminate endpoint security from the kernel. Silver Fox tooling including ValleyRAT and Winos 4.0 is referenced.
Schematic of engineered decryption failure branching into terminal command and installer paths ending in macOS persistence

Post-DEF CON Phishing Uses Malicious Google Doc to Deliver AMOS Stealer

A phishing campaign timed to post-DEF CON follow-up traffic uses a malicious Google Doc as the entry point. Targets are steered to a DecryptPanel.html lure page that serves GAPIUpdate.dmg, which installs the AMOS (Atomic macOS Stealer) payload alongside NetSupport RAT and a Ledger wallet implant. Persistence is established through a com.xdivcmp.
Schematic of CVE-2026-42271 command execution bypassing auth to read container secrets and exfiltrate API keys

LiteLLM Gateway Flaws Let Attackers Deploy XMRig on AI Infrastructure

LiteLLM sits between applications and the models they call, making it a control point worth attacking. Three vulnerabilities, CVE-2026-42271, CVE-2026-48710 and CVE-2026-49869, affect that gateway layer, with XMRig cryptomining payloads pulled down via curl and wget. AI infrastructure needs the same patch discipline and egress controls as any internet-facing service.
Schematic of phishing kit filtering personal emails and only advancing corporate credentials to OAuth token abuse

Fake Recruiter Phishing Targets Corporate Credentials on Mobile Devices

Threat actors impersonating recruiters are targeting high-value corporate credentials, with mobile devices as the delivery surface. Job-offer and hiring-themed messages reach employees on phones, where sender details are truncated, links are harder to inspect, and credential prompts look routine. The result is corporate account access obtained without a single exploit against a corporate network.

More Articles …

  1. SLEEPWALKER Backdoor Hides in dpapi.dll and Runs Bytecode on One Packet
  2. Doubloon Dredger Abuses Notion to Harvest Authentication Tokens
  3. Red Team Assessments Compare Two SOCs and BloodHound Detection Gaps
  4. Mirage2FA Abuses Microsoft 365 Login Flows at 4,500 US and EU Companies
  • 1
  • 2
  • 3
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10

Page 6 of 67

Facebook
LinkedIn
Mastodon
Bluesky
Schedule Your Assessment!

About Us

  • Privacy Policy
  • Code of Ethics
  • Sitemap
Mastodon

Areas We Serve

  • Managed IT Services Springfield, Ohio
  • Managed IT Services Dayton, Ohio
  • Managed IT Services Columbus, Ohio
Location: Springfield, Ohio · Serving Southwest and Central Ohio
Phone: (937) 319-1211
Email: [email protected]
SUBSCRIBE To Our Newsletter

Get the latest news!

Copyright © 2026 Capstone Technologies Group. All Rights Reserved.
Customized & Hosted by Capstone Technologies Group Great Hosting