Capstone Technologies Group LLC Capstone Technologies Group LLC
  • Home
  • Services
    • Managed IT Solutions
    • Cybersecurity Services
    • Data Protection & Recovery
    • VoIP Solutions
    • Website Solutions
  • Industry Solutions
    • Legal IT Solutions
    • Medical IT Solutions
    • Financial IT Solutions
    • SMB IT Solutions
    • Non Profit IT Solutions
  • Resources
    • Blog
    • White Papers
    • Threat Intelligence Center
  • About Us
    • Who We Are
    • Client Testimonials
    • Case Studies
  • Threat Intelligence Center
  • Pricing

Springfield, OH · Call (937) 319-1211

Facebook
LinkedIn
Mastodon
Bluesky
Capstone Technologies Group LLC Capstone Technologies Group LLC
  • Home
  • Services
    • Managed IT Solutions
    • Cybersecurity Services
    • Data Protection & Recovery
    • VoIP Solutions
    • Website Solutions
  • Industry Solutions
    • Legal IT Solutions
    • Medical IT Solutions
    • Financial IT Solutions
    • SMB IT Solutions
    • Non Profit IT Solutions
  • Resources
    • Blog
    • White Papers
    • Threat Intelligence Center
  • About Us
    • Who We Are
    • Client Testimonials
    • Case Studies
  • Threat Intelligence Center
  • Pricing

Contact Us

Threat Intelligence Center

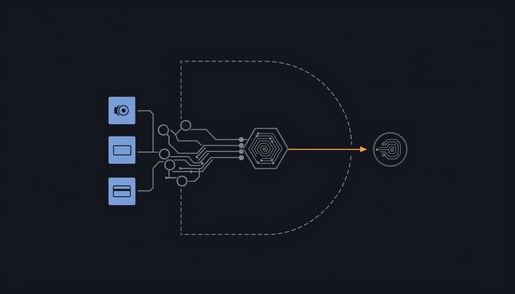
Blueprint schematic showing camera, license plate, and payment data correlated then exiting a perimeter through an uncontrolled query path

Retail Theft Bill Sparks Warnings Over Large-Scale Surveillance Powers

Legislation intended to address retail theft has prompted warnings from critics who describe the surveillance it could enable as very large and very dangerous. The debate centers on how far monitoring and data collection powers should extend, and what safeguards apply.
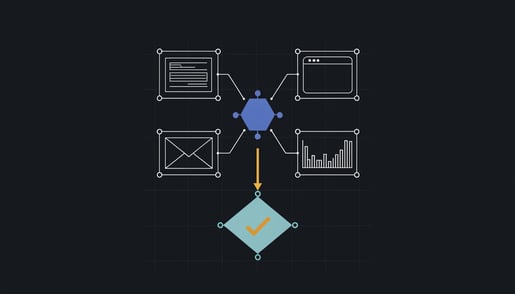
Circuit schematic showing AI-generated documents, phishing emails, fake sites and deepfake voice defeating identity verification

AI-Driven Fraud Erodes Identity Verification and Makes Deception Harder to Spot

AI has shifted fraud from a detection problem to an identity problem. Synthetic voice, video, and documents defeat the cues people were trained to trust, while attackers scale personalized deception at low cost. The practical response is verification that does not depend on how a message looks or sounds, but on controls that confirm identity independently.
Blueprint schematic of BYOVD attack unlinking kernel notification callbacks and Linux rootkit boot-order persistence

UAT-10147 Deploys SPECTRE Implant With Linux Rootkit and BYOVD Capabilities

Cisco Talos has documented UAT-10147, a Chinese-speaking intrusion actor deploying SPECTRE, a cross-platform backdoor that uses Bring Your Own Vulnerable Driver techniques to blind endpoint detection tools.
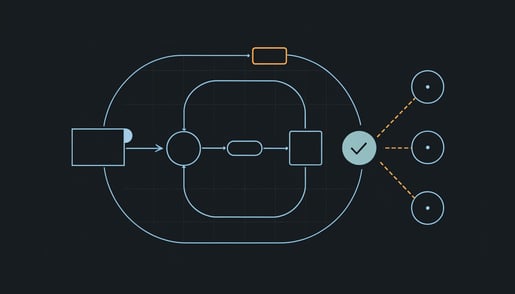
Blueprint schematic of the OAuth device code phishing flow used by EvilTokens and Kali365 phishing kits

Device Code Phishing Evolves as EvilTokens PhaaS Kit and Kali365 Emerge

Device code phishing persists because it abuses a legitimate authentication flow rather than a software flaw. Activity tied to EvilTokens and Kali365, including the EvilTokens phishing-as-a-service kit, shows the technique is still being refined and packaged for broader use. Here is how the approach has changed and what defenders and business leaders should watch for.
Schematic showing valid stolen credentials bypassing perimeter defenses to reach mail, research archives and cloud API endpoints

US Charges Iranian Hackers Over $3.4 Billion Intellectual Property Theft

The U.S. Justice Department charged 17 Iranians tied to the Mabna Institute for stealing 31.5 terabytes of academic data valued at $3.4 billion from over 100,000 professor accounts. The operation targeted 178 universities, 53 private firms, and state agencies for a decade using credential theft as its primary access method.
Schematic of MacSync Stealer chain: pasted Terminal command, credential collection, chunked upload exfiltration on macOS

Hunting MacSync Stealer Infrastructure With AppleScript and curl Pivots

MacSync Stealer relies on scripting components that defenders can turn into detection material. This analysis walks through hunting the stealer's infrastructure using behavioral pivots rather than static indicators, examining how AppleScript execution, osascript invocation, and curl network activity can be correlated to surface related hosts and follow the campaign as its indicators change.
Schematic of TWINLOOT SharePoint dead-drop polling loop and reverse tunnel reaching internal SMB and RDP services

TWINLOOT Malware Turns Microsoft Cloud Services Into Its Control Channel

Security researchers are tracking a malware family called TWINLOOT that uses Microsoft cloud services as its command-and-control infrastructure rather than attacker-owned servers. Routing instructions and data through platforms organizations already permit means the traffic reaches trusted endpoints, complicating detection that relies on blocking unfamiliar domains.

More Articles …

  1. RecruitTrap Phishing Uses Browser-in-the-Browser Popups to Steal Logins
  2. Evooo1Bot Linux Botnet Turns Routers Into Traffic Relay Nodes
  3. AI-Enabled Device Code Phishing Campaign Abuses Device Code Sign-In Flow
  4. Researcher Buys noreply.net and Companies Start Emailing Him Secrets
  • 4
  • 5
  • 6
  • 7
  • 8
  • 9
  • 10
  • 11
  • 12
  • 13

Page 9 of 67

Facebook
LinkedIn
Mastodon
Bluesky
Schedule Your Assessment!

About Us

  • Privacy Policy
  • Code of Ethics
  • Sitemap
Mastodon

Areas We Serve

  • Managed IT Services Springfield, Ohio
  • Managed IT Services Dayton, Ohio
  • Managed IT Services Columbus, Ohio
Location: Springfield, Ohio · Serving Southwest and Central Ohio
Phone: (937) 319-1211
Email: [email protected]
SUBSCRIBE To Our Newsletter

Get the latest news!

Copyright © 2026 Capstone Technologies Group. All Rights Reserved.
Customized & Hosted by Capstone Technologies Group Great Hosting