Capstone Technologies Group LLC Capstone Technologies Group LLC
  • Home
  • Services
    • Managed IT Solutions
    • Cybersecurity Services
    • Data Protection & Recovery
    • VoIP Solutions
    • Website Solutions
  • Industry Solutions
    • Legal IT Solutions
    • Medical IT Solutions
    • Financial IT Solutions
    • SMB IT Solutions
    • Non Profit IT Solutions
  • Resources
    • Blog
    • White Papers
    • Threat Intelligence Center
  • About Us
    • Who We Are
    • Client Testimonials
    • Case Studies
  • Threat Intelligence Center
  • Pricing

Springfield, OH · Call (937) 319-1211

Facebook
LinkedIn
Mastodon
Bluesky
Capstone Technologies Group LLC Capstone Technologies Group LLC
  • Home
  • Services
    • Managed IT Solutions
    • Cybersecurity Services
    • Data Protection & Recovery
    • VoIP Solutions
    • Website Solutions
  • Industry Solutions
    • Legal IT Solutions
    • Medical IT Solutions
    • Financial IT Solutions
    • SMB IT Solutions
    • Non Profit IT Solutions
  • Resources
    • Blog
    • White Papers
    • Threat Intelligence Center
  • About Us
    • Who We Are
    • Client Testimonials
    • Case Studies
  • Threat Intelligence Center
  • Pricing

Contact Us

Threat Intelligence Center

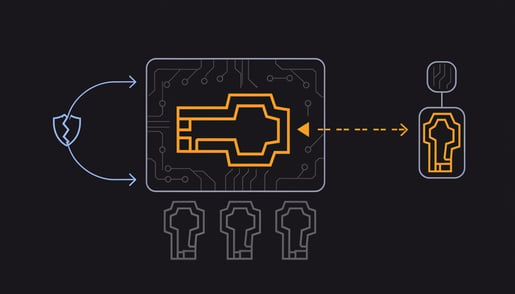
Schematic of Golden Pass-ta-key: security domain secret master key extracted from Chrome process memory

Pass-ta-key Attacks Let Malware Hijack Google-Synced Passkeys

Passkey adoption has grown on the promise that phishing-resistant credentials remove the weakest link in authentication. A newly described attack class called Pass-ta-key challenges that assumption.
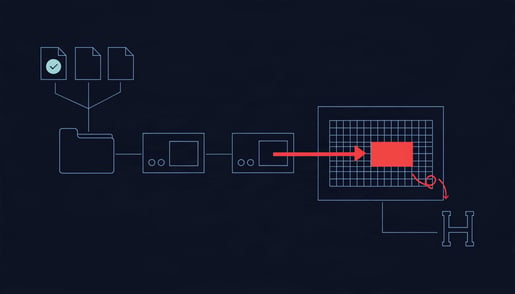
Schematic of signed AutoIT3 interpreter injecting shellcode into charmap.exe with registry Run key persistence

AutoIT Payload Injector Abuses AutoIT3 Interpreter to Drop MedusaHVNC

A recently analyzed AutoIT payload injector relies on the legitimate AutoIT3 interpreter to execute attacker-supplied script code and load follow-on malware, including MedusaHVNC and VIPKeylogger. MedusaHVNC supports hidden remote desktop control of a compromised machine, while VIPKeylogger captures credentials and keystrokes.
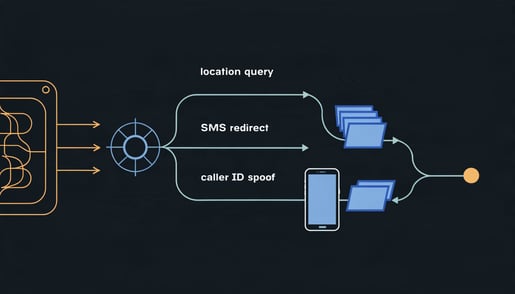
Schematic of SS7 attack path: signaling gateway redirects SMS and location queries while the target phone shows no trace

Salt Typhoon and State Hackers Target Telecom Networks Troops Rely On

State-sponsored operators attributed to China, Russia, and Iran, including the group tracked as Salt Typhoon, have made telecommunications networks a standing intelligence target. This analysis argues the harder problem is not technical discovery but implementation.
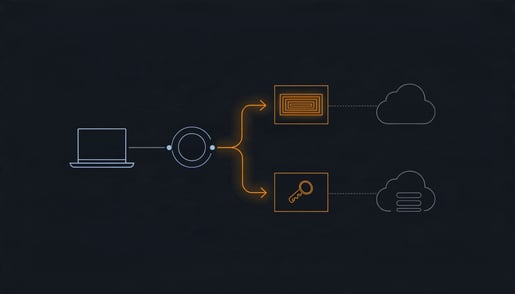
Schematic of forged DNS redirect serving fake browser update that deploys ChocoShell token-stealing malware

Hijacked Hotel Wi-Fi Pushes Fake Updates to Deliver ChocoShell Malware

Microsoft has tracked a campaign called CaptiveCrunch since early May, where attackers compromise hotel Wi-Fi gateways to push fake updates delivering CornFlake malware and ChocoShell, a PowerShell stealer targeting Microsoft 365 and Azure tokens.
Schematic of spear-phishing LNK to DLL side-loading chain deploying HollowFrame and Matryoshka backdoor

HollowFrame Loader Deploys Matryoshka Backdoor in Law Firm Spear-Phishing

Researchers have documented a spear-phishing attack against a law firm in which a loader tracked as HollowFrame was used to deploy a backdoor named Matryoshka. The pairing follows a familiar pattern: an email-delivered loader establishes the initial foothold, then unpacks a second-stage implant that gives the operator ongoing access.
Blueprint diagram of Linux PAM pam_rootok bypass allowing XMRig miner to masquerade as legitimate processes

TeamTNT Cryptominer Abuses Linux PAM to Hide XMRig From SOC Analysts

Pluggable Authentication Modules are a core part of how Linux systems verify users, which makes them an unlikely place for analysts to hunt for cryptomining. Activity attributed to TeamTNT abuses Linux PAM to conceal XMRig, keeping mining processes out of the areas SOC teams routinely inspect. Here is what the technique means for Linux server monitoring and detection engineering.
Schematic of stolen session token replay bypassing MFA gate to reach a SaaS tenant from conference Wi-Fi

Five Priorities Security Teams Should Set Before Attending Black Hat

Black Hat delivers more briefings, vendor pitches, and side events than any one attendee can reasonably absorb, which makes agenda planning the difference between a productive week and a blur of hallway conversations.

More Articles …

  1. Teams-Themed Phishing Campaign Abuses Legitimate Microsoft Login Pages
  2. Microsoft Security July 2026 Roundup of New Features and Product Updates
  3. Scattered Spider Member Indicted as Microsoft GDID Case Goes to Trial
  4. North Korea's npm Package Campaign Precedes axios Supply Chain Attack
  • 9
  • 10
  • 11
  • 12
  • 13
  • 14
  • 15
  • 16
  • 17
  • 18

Page 14 of 67

Facebook
LinkedIn
Mastodon
Bluesky
Schedule Your Assessment!

About Us

  • Privacy Policy
  • Code of Ethics
  • Sitemap
Mastodon

Areas We Serve

  • Managed IT Services Springfield, Ohio
  • Managed IT Services Dayton, Ohio
  • Managed IT Services Columbus, Ohio
Location: Springfield, Ohio · Serving Southwest and Central Ohio
Phone: (937) 319-1211
Email: [email protected]
SUBSCRIBE To Our Newsletter

Get the latest news!

Copyright © 2026 Capstone Technologies Group. All Rights Reserved.
Customized & Hosted by Capstone Technologies Group Great Hosting