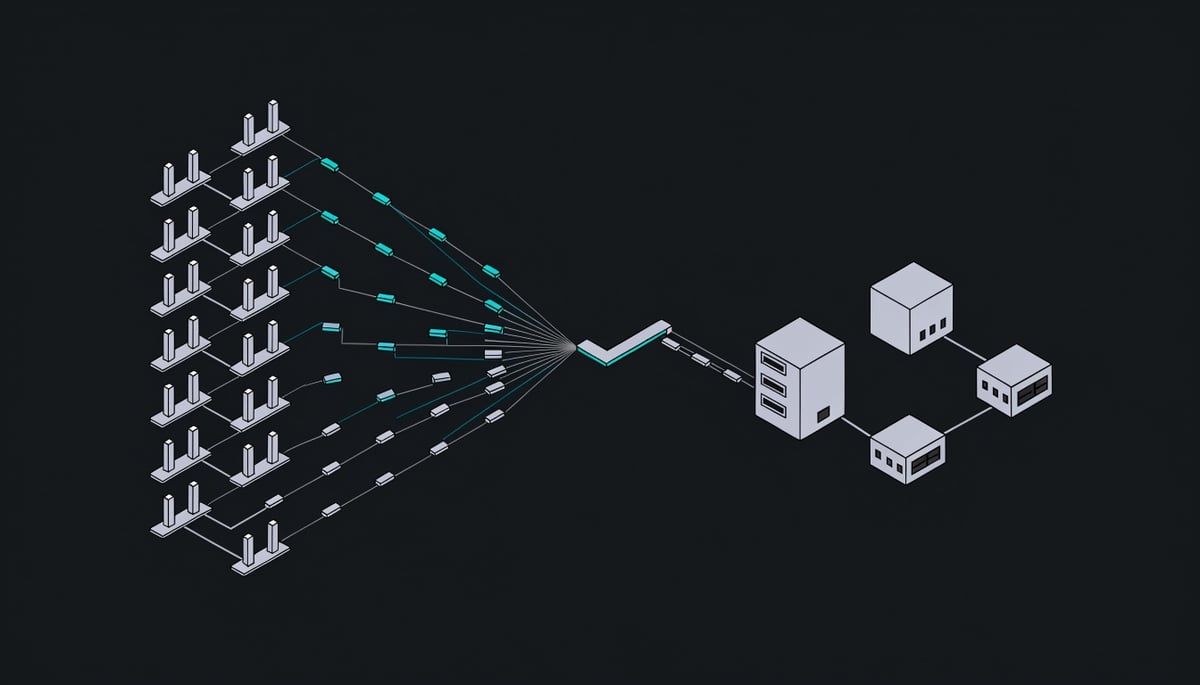
Infostealer malware such as Lumma Stealer, StealC, and RisePro now accounts for 75% of all stolen credentials, according to cybersecurity vendor Immersive, after sharp growth over the past 18 months. Those credentials include browser cookies, VPN logins, and MFA tokens, and they get sold on dark web markets to whoever wants them. Original reporting for this article comes from CSO Online.
Infostealers such as Lumma Stealer, StealC, and RisePro are now responsible for 75% of all stolen credentials, per Immersive research.
The nine trends covered here are not nine separate problems. They describe one shift: the work of breaking into a company has been split off, commoditized, and sold to the groups that do the damage. Ben McCarthy of Immersive calls it a move that enables nation-state goals through simple transactions instead of complex attacks.
You can see the same convergence on the delivery side. ClickFix lures persuade users to paste a PowerShell command into their own machines under the cover of a CAPTCHA check, which is how Huntress traced an April campaign posing as a free image editing tool to the CastleLoader loader, then to NetSupport RAT and a custom .NET stealer built to grab browser credentials, wallet extension data, and Telegram session files.
Ransomware operators sit at the end of that pipeline. After law enforcement disrupted LockBit, groups including RansomHub and Akira moved to smaller, heavily researched intrusions where encryption is the last step after full infiltration and data theft. They reach that point using purchased access, legitimate remote management software such as ScreenConnect on trial accounts, and living-off-the-land techniques.
For your business, two things follow. The cost of entry for an attacker has dropped to the price of a credential log, and the execution happens through a user action and signed administrative tools, which is exactly the activity signature-based endpoint controls were never built to flag. The sections ahead break down supply chain compromises like Shai-Hulud, polymorphic evasion, AI-assisted development, agentic attacks, and the older techniques now falling out of use.
ClickFix and the Shift to User-Executed Infection
ClickFix works by getting the victim to run the command themselves. A web page displays a familiar "verify you are human" check, then tells the user the verification failed and offers a fix: press Win+R, paste, and hit Enter. The user follows three steps that look like routine friction, and a PowerShell command executes under their own account.
The clipboard is the delivery mechanism. JavaScript on the page silently copies the command string to the clipboard when the user clicks the "I'm not a robot" element, so the victim pastes something they never typed and usually never reads in full. Operators pad the string with whitespace or a decoy comment so the visible portion of the Run dialog shows something harmless while the real payload sits off-screen.
Observed lures cover the places users already expect interruptions. Phishing pages, compromised legitimate sites, fake browser update notices, and document verification screens all carry the same three-step instruction block. Huntress logged a ClickFix lure in April dressed up as a free image-editing tool, which pulled in a loader called CastleLoader before the chain dropped NetSupport RAT and a custom .NET stealer aimed at browser credentials, wallet extension data, and Telegram session files.
The reason this gets past layered file controls is procedural. Mark-of-the-Web tags files that a browser or mail client writes to disk, and none of that applies to a string pasted into a shell. There is no attachment for your mail gateway to detonate and no download for reputation scoring to rate, because the first artifact on disk is fetched by a signed Windows binary acting on an instruction the user approved.
The execution leaves a recognizable trail, even though the initial vector produces no inbound file:
- Entries under
HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\RunMRUrecording what was typed into the Run dialog - PowerShell command lines using
-encor-EncodedCommandwith base64 blobs, often with-w hidden mshta.exeinvoked against a remote URL to pull and run script contentcurl.exeorcertutilwriting a payload into a user-writable temp directory- A process tree where
explorer.exeis the parent ofpowershell.exeormshta.exe, which is unusual outside of hands-on-keyboard activity
In ATT&CK terms this is User Execution (T1204) feeding directly into Command and Scripting Interpreter: PowerShell (T1059.001), with Signed Binary Proxy Execution via Mshta (T1218.005) where the operator prefers HTA over a direct script call. The practical effect is that the first malicious action on the endpoint is attributable to a legitimate user session, which slows triage because the activity does not look like an intrusion until the second stage lands.
Second-stage payloads skew toward commodity credential theft and remote access, including stealers of the Lumma Stealer and StealC class alongside RATs such as NetSupport. Jim Walter of SentinelLABS describes the technique as "simple, effective, and increasingly common," noting its spread across phishing sites, compromised webpages, and broader social engineering campaigns.
For a business, the cost is the same as any credential compromise with a faster path to it. Stolen session cookies and tokens let an attacker resume an authenticated session against your SaaS and VPN estate without re-authenticating, and a RAT on a finance or admin workstation gives interactive access to whatever that user can reach. The technique scales because it needs no vulnerability, only a page that looks like a verification step.
CastleLoader, Infostealers and the Credential Supply Chain
CastleLoader sits in the middle of the chain as a distribution hub, not a payload in itself. In the April campaign logged by Huntress, the loader arrived behind a lure posing as a free image-editing tool, then pulled down two distinct follow-on components: NetSupport RAT, a legitimate remote administration product repurposed for hands-on access, and a custom .NET stealer. One loader, two capabilities, delivered to the same host in a single run.
The stealer handles collection. Its stated targets were browser credentials, wallet extension data, and Telegram session files, which maps to T1555.003 (credentials from web browsers) and T1539 (steal web session cookie). That second category matters more than the first for most businesses.
A saved password can be rotated. A stolen session cookie represents an authentication event that already happened, so replaying it into an attacker-controlled browser (T1550.004) lands the attacker inside the account without ever touching the login prompt or the MFA challenge. If your staff keep long-lived sessions open to Microsoft 365, a VPN portal, or a cloud console, the cookie is the asset.
The families named by Immersive, Lumma Stealer, StealC, and RisePro, operate on the same collection model at commodity scale. Beyond browser material they pull VPN credentials, MFA tokens, and crypto wallet data, package it as a log, and push it to criminal markets. The person who infects the laptop is frequently not the person who uses the access.
That separation is the part worth understanding. A buyer browsing a stealer marketplace is not shopping for a laptop, they are shopping for a corporate VPN credential or a cloud session belonging to an employee with the right access. RansomHub and Akira affiliates, who moved toward smaller, highly targeted intrusions after the law enforcement action against LockBit, fit that buyer profile well. Per Immersive's Ben McCarthy, these groups invest in reconnaissance and tailored attack development, and purchased access shortens the first phase of that work considerably.
Encryption comes last in their sequence. Full infiltration and data exfiltration happen first, with the extortion leverage sitting in the stolen data rather than in the locked files. For your business that reorders the damage: the information is gone before any ransom note appears, which is why data theft and threatened public leaks now drive the negotiation.
The Shai-Hulud attacks apply the same credential logic to development infrastructure. The malware was self-propagating, stole CI/CD secrets, and hijacked GitHub Actions OIDC tokens so that malicious package versions were published through the victims' own release pipelines (T1195.002). The build system's own identity signed the compromise.
The Axios compromise followed a parallel route. Attackers went after the lead maintainer's credentials and inserted a malicious dependency into legitimate releases, which caused downstream dependencies to download remote-access malware matched to the victim's operating system, according to Huntress principal technical writer Lindsey O'Donnell-Welch.
Taken together, the pipeline runs from a single user-executed loader through credential and session collection, into a marketplace listing, and then into the hands of an affiliate who already knows how to monetize enterprise access. One infected laptop, or one maintainer account, is a workable starting point for network-wide encryption.
Legitimate Remote Access Tools as Attacker Infrastructure
ScreenConnect is a commercial remote support product, and that is exactly why attackers run it. Huntress threat intelligence analyst Adam Brown notes that threat actors frequently stand up their own tooling on trial accounts, which means the client dropped onto an endpoint is a genuine, vendor-signed build pointing at an attacker-controlled instance. MITRE tracks this as T1219 (Remote Access Software), and it sits in the intrusion chain where a custom RAT used to sit.
NetSupport Manager follows the same pattern. It is a long-established remote administration product with full session control, file transfer, and command execution built in, so an operator who installs it inherits hands-on-keyboard access without writing a line of implant code.
Allow-listing struggles here because there is nothing to disallow. The binary carries a valid vendor signature, its hash matches a known-good file, and in many environments that software category is already whitelisted because the IT team or an outsourced provider uses a product like it. Unit 42's Alex Hinchliffe makes the point about hash-based scanners being thwarted by recompilation, and the inverse applies in this case: the hash is stable, legitimate, and reputationally clean.
The network side is equally quiet. Brown describes attackers covering command-and-control and exfiltration routes under Cloudflare accounts, with free cloud hosting removing any need for bulletproof hosting providers. Outbound traffic resolves to a well-known CDN over TLS, which blends into the same egress your business applications already generate.
What separates a malicious instance from a sanctioned one is ownership and provenance rather than content. A few markers tend to hold:
- Relay and control domains that belong to an unfamiliar tenant instead of the organization's licensed instance
- Instance or client IDs that appear nowhere in the deployment inventory
- Installation timestamps falling outside approved change windows, often minutes after a user-executed script
- Deployment by a path other than the normal management console, including installs initiated under a standard user context
- Session activity originating from geographies or hours that do not match the support team's coverage
This matters operationally because remote management traffic is usually treated as routine. An attacker session logged alongside genuine helpdesk work does not stand out in a ticketing review, which extends the period before anyone investigates.
ExtraHop's Jamie Moles reports a notable uptick in cloud-based services and remote management platforms appearing inside ransomware toolchains, and the same tooling turns up in Akira and RansomHub intrusions. Both groups treat encryption as the final step after full infiltration and data exfiltration, so the remote access tool is the working surface for reconnaissance, collection, and staging.
Before encryption runs, operators disable protections using legitimate executables, including signed system drivers and remote management software, which maps to T1562.001 (Impair Defenses). With defenses off and a licensed access tool already in place, the step from established access to T1486 (Data Encrypted for Impact) is short and requires no custom payload.
For your organization, the practical consequence is that the intrusion and the recovery both involve software your own staff may legitimately run. Incident scoping has to separate authorized sessions from attacker sessions across the same product, which lengthens investigation time and complicates the question of what data left the network before encryption.
Operational and Organizations Consequences for Organizations
Credentials bought from a market do not look like an intrusion when they are used. An attacker signing into your mail tenant with a valid session arrives as a legitimate user, reads months of invoice threads, and then changes payment details on an in-flight transaction. Your finance team approves a wire that matches a real conversation with a real supplier, and the money is gone before anyone queries it.
The ransomware groups named earlier run a different clock. Akira and RansomHub treat encryption as the final step after full infiltration and data exfiltration, which means that by the time your files lock, the data has already left. Paying for a decryption key does nothing about the copy they are threatening to publish.
That second lever is where the compliance cost sits. A confirmed theft of personal data triggers notification duties under GDPR and, depending on your sector, separate reporting lines for health, financial, or critical infrastructure operators. Healthcare remains a top target precisely because the urgency of patient care pushes payment decisions faster, and critical infrastructure is facing the same pressure.
Check how your cyber insurance policy treats this. Insurers increasingly ask what controls were in place at the point of entry, and an incident that started with a purchased login or a remote access client nobody authorized can become a slow claim conversation. Your customer contracts may also carry notification windows shorter than the regulatory ones, so a single breach can put you in front of three different audiences in the same week.
If you ship software, the exposure runs the other way. The Shai-Hulud attacks stole CI/CD secrets and hijacked GitHub Actions OIDC tokens to publish malicious package versions through victims' own release pipelines, which means the poisoned build carried the victim's signature and reputation. In the Axios compromise, attackers took the lead maintainer's credentials and inserted a malicious dependency into legitimate releases, and downstream users pulled remote access malware tailored to their operating system.
Your customers become the casualties in that scenario, and your incident response turns into a recall. You are contacting every organization that consumed an affected version, and your engineering team is reconstructing which builds were clean while your release pipeline stays frozen.
Three groups carry more of this risk than others:
- Organizations where ordinary users hold local administrator rights, because a pasted command or a stolen session inherits those rights immediately.
- Environments with unmanaged remote access tooling, where an additional vendor-signed client raises no questions from anyone.
- Development teams holding long-lived, high-privilege tokens for package registries and build systems, where one maintainer account reaches every customer.
Recovery time is also shifting. Barracuda reports growing use of Rust and Go in ransomware binaries, letting one codebase cover Windows, Linux, and virtualization environments, so an attacker who reaches your hypervisor can encrypt the hosts and the guests in the same pass. If your virtual infrastructure and your backup infrastructure share that layer, the restore you planned for may not be available.
JadePuffer showed an agentic attack carrying out destructive actions with limited evidence of human control, including adapting when it hit obstacles. The practical consequence is a compressed window between first access and damage, which leaves less time for a human analyst to interrupt the sequence.
Detection and Hardening Steps That Address These Techniques
Start with the Run dialog. Where your user population has no business need for it, disable it through Group Policy (User Configuration, Administrative Templates, Start Menu and Taskbar, "Remove Run menu from Start Menu"), which removes the paste-and-execute path that user-driven lures depend on. Where you cannot disable it outright, treat the Run history as a hunting source.
Pull HKCU\Software\Microsoft\Windows\CurrentVersion\Explorer\RunMRU across your estate and look for entries containing powershell, mshta, curl, or base64-looking strings. Pair that with process creation logs (Event ID 4688 with command line auditing enabled) and alert on any powershell.exe or cmd.exe whose parent process is a browser or explorer.exe carrying an -enc or -EncodedCommand argument. Those two queries together catch the delivery stage before a loader reaches disk.
Next, inventory remote administration software. Query installed services and running processes for every remote support agent in your environment, then compare that list against what your IT team actually sanctioned. Any agent pointing at an instance you do not own gets removed and the host investigated, because a vendor-signed binary will not trip reputation checks on its own.
For any endpoint with a confirmed stealer infection, a password reset alone leaves the attacker logged in. You need to revoke refresh tokens and active sessions in your identity provider at the same time, force reauthentication, and review OAuth app consents granted from that account. Adlumin, deployed in environments Capstone manages, flags the authentication anomalies that follow stolen session material, including impossible travel and sign-ins from infrastructure your users have never touched.
Over the next few sprints, work through the controls that reduce the value of stolen credentials and scripted execution:
- Move privileged and remote-access accounts to phishing-resistant MFA (FIDO2 security keys or platform passkeys) and shorten session lifetimes so a stolen cookie expires sooner.
- Enable PowerShell script block logging (Event ID 4104) and module logging, and apply constrained language mode for standard users so pasted scripts fail on .NET and COM calls.
- Block unapproved remote access and tunneling domains at the proxy or DNS layer, allow-listing only the support tooling your team uses.
- Pin dependencies to exact versions with lockfiles, disable post-install scripts in CI where practical, and scope GitHub Actions OIDC trust policies to specific repositories and branches.
- Rotate every CI/CD secret, npm publish token, and registry credential after any suspected pipeline exposure, and audit which packages your release process is authorized to publish.
The longer-term work is structural. Remove local administrator rights from standard users so infostealers and loaders run in a limited context and cannot disable endpoint agents or install drivers. Segment your network so that backup servers, hypervisor management interfaces, and domain controllers sit behind separate authentication boundaries from general user subnets, which slows the lateral movement step that precedes encryption.
Then test recovery rather than assume it. Restore a representative server and a production database from offline or immutable copies on a schedule, time the restore, and document what broke. Run a tabletop exercise that assumes data was exfiltrated before encryption, since that scenario drives legal notification and customer communication work your technical recovery plan probably does not cover. Record the restore times and gaps you find, and use them to set your next round of priorities.
Priorities for the Next Review Cycle
The techniques that fell out of use tell you as much as the ones rising. Exploit kits, Office macros, USB-borne malware, traditional botnets, and network worms like Conficker all declined because segmentation, automated patching, and endpoint defenses made them unreliable. Attackers did not find a better exploit. They stopped needing one.
What replaced those methods runs on functionality your business already trusts and already permits:
- Signed system drivers and legitimate administrative binaries used to disable defenses before anything noisy happens
- Package repositories and release pipelines, where a maintainer's stolen credentials put malicious code inside builds you pull on purpose
- Free cloud hosting and trial licenses standing in for paid criminal infrastructure
- Commercial LLM accounts, often stolen or resold, writing loaders, droppers, and admin panels
Rust and Go give ransomware operators one code base that targets Windows, Linux, and virtualization hosts. Polymorphism and commodity packers mean the same program produces a different hash every time, so a file fingerprint tells you very little. JadePuffer showed an attack conducting its own reconnaissance and adapting when it hit obstacles, with limited evidence of human control. The direction of travel is toward less bespoke tooling and more autonomy.
The judgment call worth settling before your next review is how your team classifies an infostealer hit. Treat any infostealer detection on any endpoint as a confirmed credential compromise affecting every account and session that touched that machine, including the active tokens, not just the passwords. That classification decision is the hinge. It is the point where a commodity infection either ends or becomes someone else's valid login into your environment weeks later.